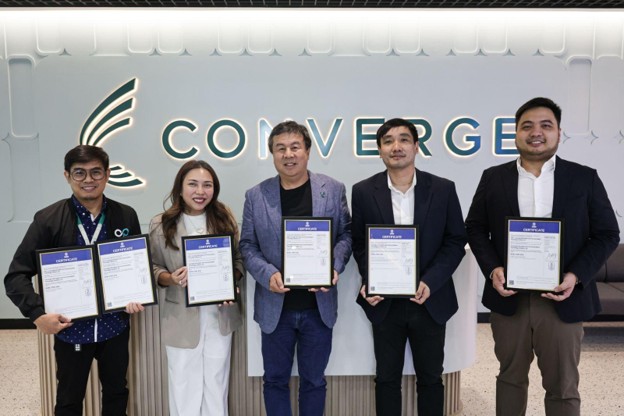





Converge ICT Solutions Inc. has secured the ISO/IEC 27001:2022 certification for its Information Security Management System (ISMS), reinforcing its efforts to protect customer information and strengthen cybersecurity across its operations.
Awarded by Bureau Veritas, the internationally recognized certification validates Converge’s implementation of information security practices designed to identify risks, protect sensitive data, and continuously improve its security management systems.
The ISO/IEC 27001:2022 standard provides a framework for establishing, implementing, maintaining, and improving an organization’s information security management system. It addresses the growing need for data protection, privacy, operational resilience, and security as businesses become increasingly dependent on digital services.
Converge Corporate Compliance, Data Protection, and Corporate Sustainability Officer Atty. Laurice Esteban-Tuason said protecting customer information is a fundamental responsibility for the company, which handles substantial volumes of data as a broadband provider serving millions of subscribers.
The certification also strengthens Converge’s ability to serve industries with stringent data security and compliance requirements, including business process outsourcing (BPO) companies and financial institutions.
The milestone supports the company’s broader transformation from a telecommunications provider into a technology company, as it expands its enterprise portfolio beyond connectivity and strengthens its business-to-business (B2B) services.
Converge SVP and Head of Corporate Information Security Office Andrew Malijan said the company will continue enhancing its security practices to address emerging risks and evolving cyber threats.
Through its adoption of the international standard, Converge aims to reinforce customer trust and strengthen its position as a provider of secure digital connectivity and enterprise technology services.